

In one of the most severe financial sector penalties ever handed down in East Asia, South Korea’s Personal Information Protection Commission (PIPC) has imposed an administrative fine exceeding $12 million (approx. 16+ billion KRW) on Lotte Card. Following an exhaustive forensic investigation into catastrophic customer data leaks, the ruling sends an unmistakable shockwave across APAC banking and fintech sectors: under the aggressively overhauled Personal Information Protection Act (PIPA), systemic technical negligence and inadequate vendor supervision will trigger corporate penalties proportional to total turnover.
The Breach Anatomy: How Lotte Card's Defenses Crumbled
The PIPC investigation exposed critical vulnerabilities in Lotte Card’s identity lifecycle and internal database architecture. The unauthorized exfiltration compromised names, resident registration numbers, credit card limits, and payment authentication credentials belonging to millions of account holders.
Forensic audits revealed three compounding failures that directly precipitated the incident:
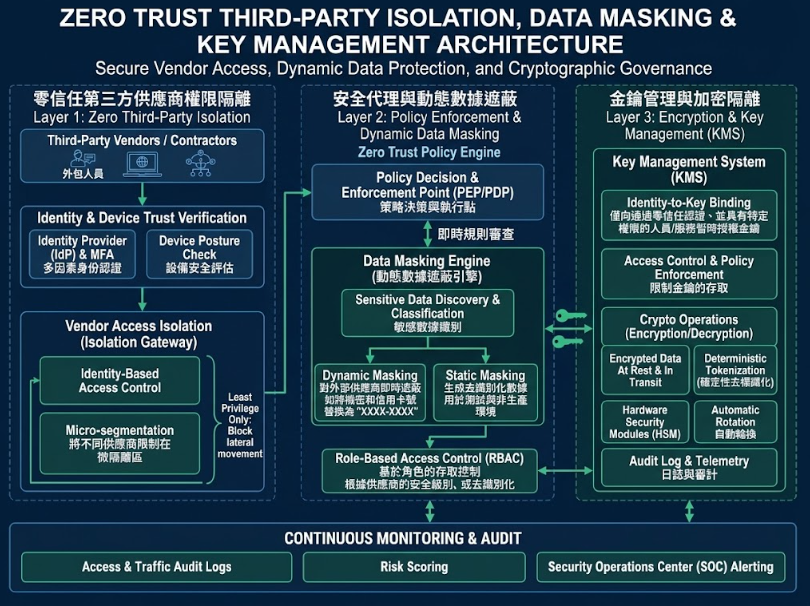
- Unrestricted Third-Party Contractor Access: External system integration contractors were granted excessive privileges to production databases containing unmasked, plain-text financial identifiers.
- Deficient Encryption and Endpoint Protection: High-risk customer datasets were transferred across internal network endpoints without cryptographic tokenization, allowing external portable media to export sensitive records without triggering Data Loss Prevention (DLP) alerts.
- Failure of Mandatory Access Logging: Audit logs tracking database queries were either truncated or disabled, leaving security operations teams blind to unauthorized bulk downloads for multiple weeks.
The Regulatory Shift: South Korea's Reformed PIPA Enforces Turnover-Based Fines
Historically, data protection penalties across East Asia were capped at fixed statutory ceilings that enterprise balance sheets easily absorbed as a mere cost of doing business. The Lotte Card landmark penalty cements the operational teeth of Korea’s amended PIPA framework:
1. Revenue-Proportional Fines (Up to 3% of Total Turnover)
Under statutory revisions, the PIPC calculates administrative fines based on an enterprise's global or total annual turnover—excluding only revenue demonstrably unrelated to the breached processing activities. This mirrors the aggressive enforcement posture of the European Union's GDPR.
2. Strict Strict-Liability for Outsourcee Negligence
PIPA explicitly holds data controllers vicariously liable for the security infractions of their processors and contractors. Claiming that "a contractor breached internal policy" provides zero statutory defense; controllers must prove continuous technical auditing and contractual enforcement.
3. Personal Civil and Criminal Exposure for Executives
Beyond institutional fines, regulatory bodies in South Korea actively recommend administrative sanctions, professional disqualification, and referral for prosecution against Chief Privacy Officers (CPOs) and Chief Information Security Officers (CISOs) where willful negligence is established.
Actionable Blueprint: Fortifying APAC Financial & Enterprise Cloud Silos
As privacy regulators across South Korea, Singapore, Australia, and Hong Kong converge on strict technical baseline enforcement, Chief Technology Officers and DPOs must implement four non-negotiable safeguards:
- Institute Continuous Zero-Trust Verification for Third Parties: Revoke perpetual VPN and privileged database access for contractors. Enforce ephemeral, just-in-time access tied to specific ticketed maintenance windows.
- Mandate Ubiquitous Field-Level Tokenization: Ensure sensitive fields—such as credit card numbers, national identification tokens, and salary records—are encrypted at rest, in transit, and strictly masked in query outputs.
- Automate Tamper-Evident Security Information Management: Implement write-once-read-many (WORM) audit logging that flags anomalous bulk queries, off-hours database dumps, or unwhitelisted outbound file transfers.
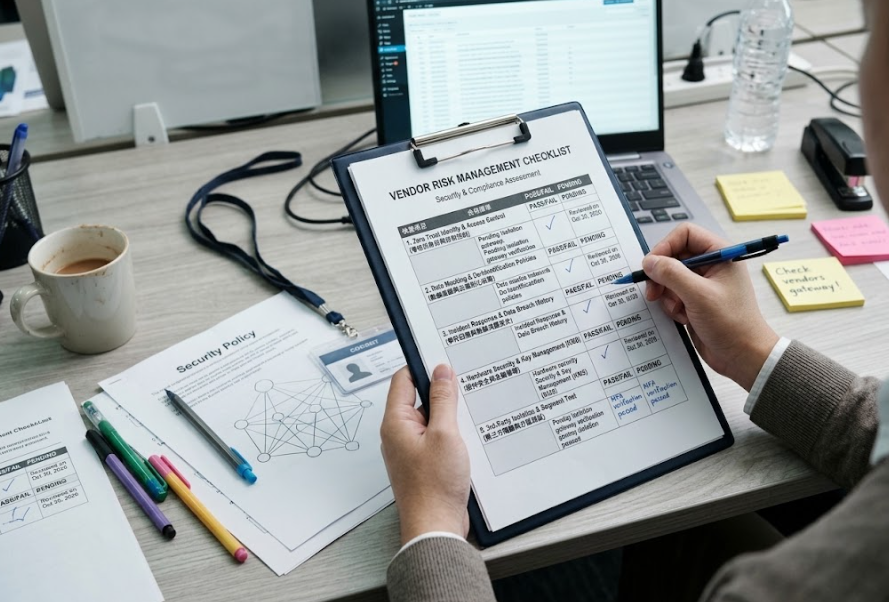
- Execute Rigorous Third-Party Privacy Audits: Move beyond static vendor questionnaires. Deploy programmatic posture assessments and automated compliance scanning to verify outsourcee security health.
Secure Your Enterprise Against Costly Breaches and Multi-Million Dollar Fines
Are your third-party vendor connections, cloud databases, and customer identity architectures fully insulated against unauthorized exfiltration and APAC regulatory enforcement?
Meta Connects Asia delivers specialized financial privacy engineering, third-party risk management (TPRM) audits, and cross-border data protection roadmaps tailored for enterprise leaders across APAC.